
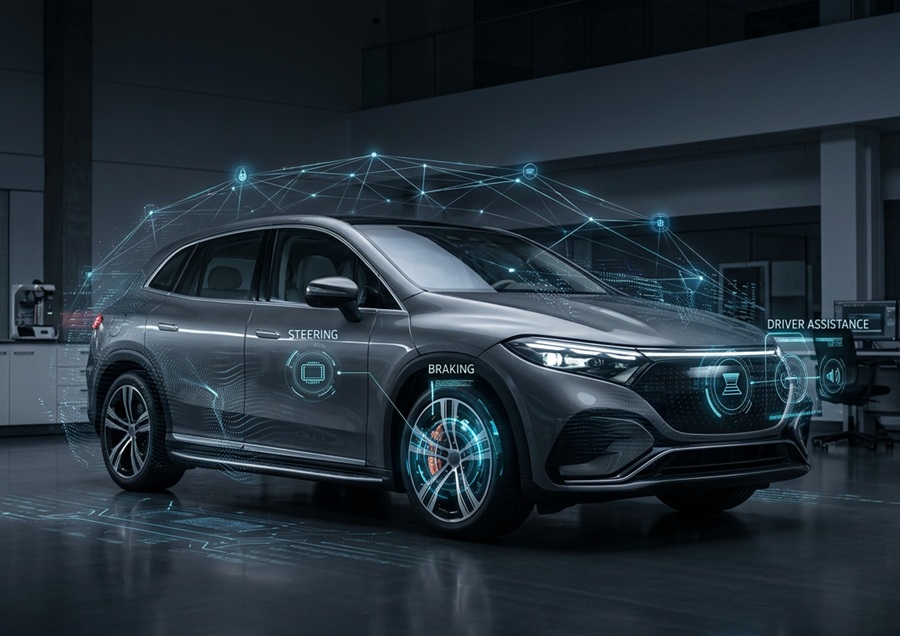
Software-defined vehicles face a growing risk of cyberattack, but many of the systems that matter most for safety still cannot be fixed remotely, according to the eSync Alliance. When a flaw is found in a brake, steering or driver assistance controller, the fix often depends on the owner bringing the car to a workshop, which could leave the vehicle exposed for months.
Most carmakers’ over-the-air update systems were designed around the infotainment screen and the telematics unit. The controllers that handle braking, steering and driver assistance usually come from separate specialist suppliers, each with its own way of receiving software. Many are updated only at a service, or not at all.
Developers expect the threat to grow. In a recent survey by automotive software company QNX, 83% of automotive software developers said they expect software-defined vehicles to become a major target for cyberattacks within the next three years.
The risk is not hypothetical. In 2025, researchers disclosed a set of flaws, known as PerfektBlue, in a Bluetooth software component supplied to several carmakers, and used them to break into the infotainment systems of Volkswagen, Mercedes-Benz and Skoda models. The supplier released a fix in September 2024, but it had to pass through the head unit maker and the carmaker before reaching dealers, and some vehicles may still have been unpatched almost a year later.
Mike Gardner, Executive Director of the eSync Alliance, said: “A security flaw in a brake or steering controller is exactly what an attacker would look for, and today it is often the hardest thing to fix. If the only way to patch it is a recall, every car stays exposed until its owner books it in, and some never will.”
“It does not have to be that way. A common update standard across suppliers lets a carmaker reach every controller in the vehicle through one secure channel and fix them together. That approach is already running at production scale on selected models in production in nations all over the world, and it needs to become the norm before the attacks arrive, not after.”
About the eSync Alliance
The eSync™ Alliance is a non-profit trade association driving a multi-company solution for Over-the-Air (OTA) updates and diagnostics data in the automotive electronics space. Used in millions of vehicles around the world, eSync has the power to save auto makers and the supply chain millions by offering the only standardized OTA bi-directional data pipeline that is proven for remote software updates, diagnostics, and telematics. OEMs can access an easy, effective, and secure platform that is ready to be integrated into vehicles. Tier-1 suppliers are not required to spend time and resource re-engineering their product to meet a multitude of different OTA protocols. Learn more at: esyncalliance.org
 Finite State & RKVST Partner to Accelerate Software Transparency
 Apliqo launches two new software solutions
 New software launched to help drive expansion for Progrex
 How Entity Management Software Keeps Corporate Records in Order
- Separating Staging and Production for a Small SaaS Team
 Trade Tech Survey Uncovers Continued Lack of Preparedness for ICS2-ENS & EORI Compliance